Zero-knowledge encryption for your notes
A zero-knowledge notes app is one whose operator cannot read your notes — not because of a policy, and not because nobody has looked yet, but because the keys that would open them were never sent anywhere. This page explains what that means in practice, how Scrinium implements it, and what it costs you.
Updated October 2026
The short answer
Zero-knowledge encryption means the service storing your notes cannot read them: the keys never leave your device, so a breach, an employee or a legal request yields ciphertext and nothing else. Most apps that say “encrypted” encrypt at rest with keys they manage, which protects a stolen disk but not you from the service. Scrinium is built the other way. Your password derives a Master Unlock Key with Argon2id (3 iterations, 64 MiB of memory, a 16-byte salt); that key unwraps a 32-byte account key, then a vault key, then a unique key per note. Every note body, title and attachment is sealed with XChaCha20-Poly1305 using a 24-byte nonce, and no key material is written to disk. The server stores encrypted blobs, an SRP-6a verifier and your email address. The practical test: if the operator can reset your password by email, it can read your notes.
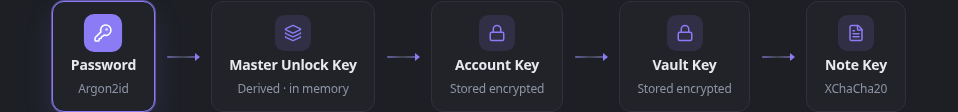
What does zero-knowledge encryption actually rule out?
The phrase is used loosely, so it is worth being concrete. For a notes app to be zero-knowledge, the operator must be unable to produce the plaintext of your notes in response to a request — from itself, from an employee, from an attacker who has taken the database, or from a court. That rules out three things that are common elsewhere: escrow keys held “for compliance”, a server-side admin view that exists but is “only used for support”, and any feature that must read your notes to work.
It does not mean the service stores nothing. It stores ciphertext, and it has to store enough to authenticate you. The question is whether what it holds is useful to anyone who takes it.
Why are most “encrypted” note apps not zero-knowledge?
“Encrypted at rest” is about a stolen disk. The service holds the key, encrypts the database with it, and can decrypt whenever it needs to — for a support ticket, an abuse investigation, a legal request, or an AI feature that summarises your notes. Nothing about that is dishonest, but it is a different promise from the one people hear when they read the word “encrypted”.
A quick way to tell the two apart: ask who can reset your password. If an email link can restore access to your notes, then the operator can read them. If it cannot — if losing your password means losing the key — the encryption is real, and the inconvenience is the receipt.
How does Scrinium implement zero-knowledge encryption?
The key hierarchy follows the model used by password managers rather than the one used by note apps: nothing is encrypted with your password directly, and no single key does more than one job.
- Your password never leaves the browser. Login uses SRP-6a, a protocol in which the server verifies a proof instead of receiving the password — and authenticates itself to you in return.
- Argon2id derives a Master Unlock Key. 3 iterations over 64 MiB of memory with a 16-byte salt. Memory-hard key derivation makes bulk guessing expensive, which matters precisely because an attacker who steals the database has the ciphertext offline.
- That key unwraps an Account Key, then a Vault Key. Changing your password re-wraps the hierarchy rather than re-encrypting your notes.
- Every note gets its own 32-byte key. A note key is generated per note and wrapped by the vault key, so one compromised note tells an attacker nothing about the others.
- Everything is sealed with XChaCha20-Poly1305. An authenticated cipher with a 24-byte nonce, so tampering is detected on decrypt rather than silently rendered. Attachments get the same treatment under their own keys, capped at 5 MiB each.
- Keys exist in memory only. No key material is written to localStorage, sessionStorage, or IndexedDB. Notes at rest on disk are stored encrypted too.
The design is documented in full, not summarised in a marketing paragraph — see the cryptography design for the primitives and the wrapping order, and the threat model for what this does and does not protect against.
What does Scrinium’s server store?
Opaque ciphertext. No key, no plaintext, no metadata about what is inside.
Used for mutual authentication. It is not a password hash and cannot be replayed to log in.
Encrypted under your password-derived key — unreadable without the password.
For account verification and recovery. Everything else about you is optional.
What are the trade-offs of zero-knowledge encryption?
Nobody can reset a password they cannot read the key for. Recovery happens through the recovery key you are given when the vault is created, not through an email link.
If the password and the recovery key are both lost, the ciphertext is unreadable by anyone — including us. That is the same property that protects the notes, viewed from the other side.
Keys live in memory only, so a refresh or a restart asks for the password again. It is not a broken session; a session that outlived the key is exactly what we refuse to ship.
No server-side search, no server-side image processing, no “AI summarise this note”. Features that would need your plaintext are built on the device instead, or not built.
These are the costs, and they are the reason a product like this is worth choosing deliberately rather than by default. If a note app you use can restore your access with an email link, it is not zero-knowledge — which is fine, as long as it is not being sold as though it were.
Questions people ask
What is a zero-knowledge notes app?
A notes app where the operator cannot read your notes even if it wanted to, because the decryption keys never leave your device. The server stores ciphertext and a way to authenticate you, nothing more.
Is end-to-end encryption the same as zero-knowledge?
They overlap, but the words are not interchangeable. End-to-end encryption describes how data travels between you and your devices; zero-knowledge describes what the operator can know. A service can encrypt notes in transit and still hold the keys at rest. Zero-knowledge means it holds neither the keys nor a working copy.
Can Scrinium read my notes?
No. Note bodies and titles are encrypted on your device with a per-note key wrapped by a vault key that exists only in your browser’s memory. The server receives ciphertext, and there is no escrow key, back door, or admin view that can open it.
What happens if I forget my password?
You use the recovery key issued when you created the vault; it can unwrap your account key independently of the password. If the password and the recovery key are both lost, the notes are unrecoverable by design.
Is client-side encrypted note-taking usable day to day?
Yes — the trade is fewer server features, not a worse editor. Scrinium renders Markdown inline as you type, searches locally over decrypted notes in memory, and syncs encrypted blobs free and unlimited across devices.
Create a vault and watch the network tab: encrypted blobs leave the device, and nothing else does.